
GRC Consulting
Create structure. Strengthen security.
We support companies in establishing, developing, and reviewing their information security management system (ISMS) — with a pragmatic, effective approach aligned with their goals.
 Establish an ISMS
 Gap analyses
 Review an ISMS
 Implement compliance requirements
Our expertise for your role
GRC consultants
You advise companies on implementing compliance and security requirements. We support you with tools and expert knowledge tailored to your consulting engagement.

CISOs & information security leads
You are responsible for information security in your company. We help you establish, develop, and review an effective ISMS.
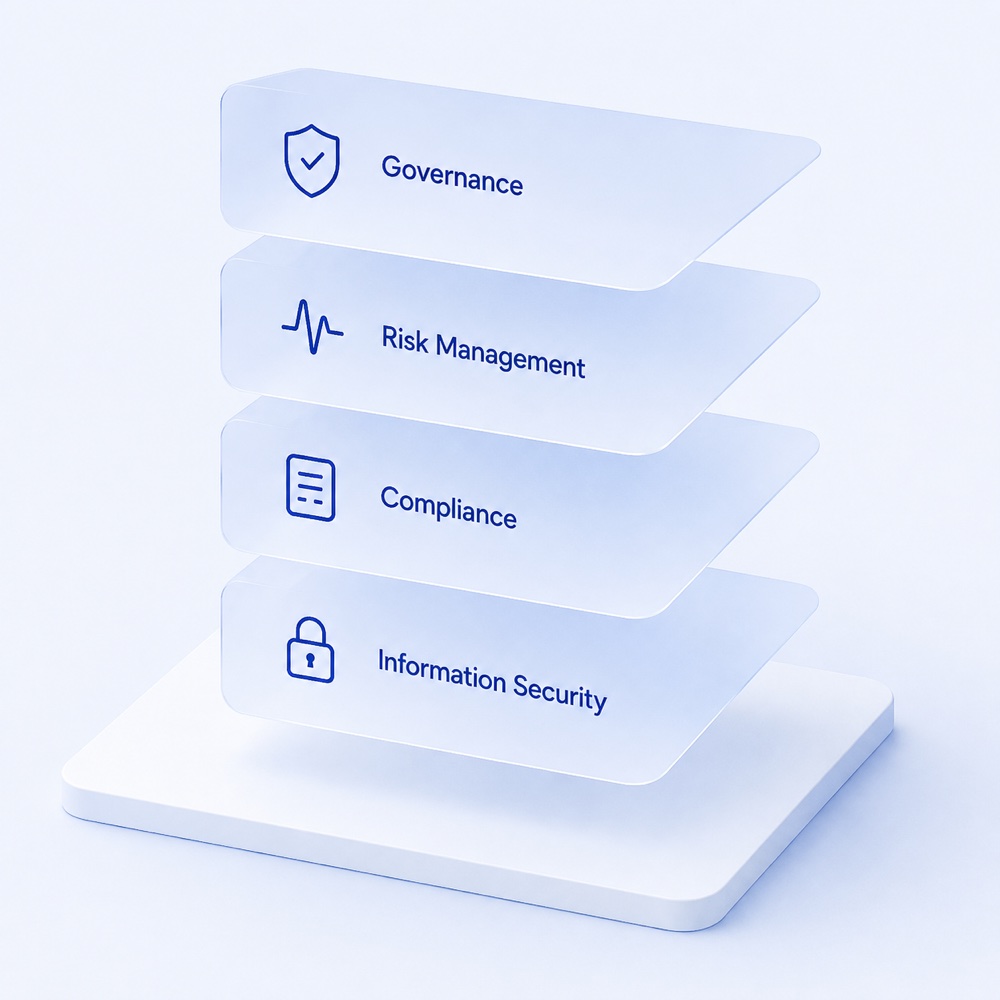
Security strategy & governance
Governance determines who decides, which risks are accepted, and how security is anchored in the organization.
- Align security objectives and responsibilities with the company strategy.
- Clarify roles, decision paths, and policies so they hold up in daily work.
- Embed the implementation and development of your ISMS in your organization.
Your outcome: You receive a clear governance structure and prioritized next steps for your security strategy.
Risk management & assessments
Risks become manageable once they are named, assessed, and turned into action.
- Identify and assess the information security and compliance risks that matter to you.
- Use assessments to show the distance to requirements such as ISO 27001 and NIS-2.
- Turn the findings into a prioritized action plan.
Your outcome: You see where the largest gaps are and which measures will have an effect first.
Compliance & regulation
An effective ISMS connects requirements with working processes and reliable evidence. We help you review implementation progress and embed the necessary improvements in your organization.
- Analyze documents and evidence to identify gaps against relevant requirements.
- Align policies, processes, and responsibilities to establish and develop your ISMS.
- Review your existing ISMS for traceable implementation and reliable evidence.
- Interpret findings and translate them into prioritized actions for your company.
Your outcome: You receive a clear picture of the areas that need attention and an agreed action plan. We support you in putting the next steps into practice within your organization.
From initial assessment to implementation
Understand
We review your goals, the existing organization, and the requirements that apply to you. Together, we define the scope of the engagement.
Assess
We evaluate gaps and risks and derive prioritized measures from them.
Support
We support implementation, clarify responsibilities, and stay involved in the expert judgment.
Let’s get started together.
Whether you need to establish an ISMS, analyze gaps, review your ISMS, or get strategic advice: let’s discuss your starting point and a useful next step for GRC and information security.
Arrange a consulting call